Service capability

Cybersecurity Services & Audits

Watabe Digital offers comprehensive cybersecurity audits, vulnerability scanning, penetration testing, and IT compliance services for Tanzanian organizations.

  • Dar es Salaam based
  • Tanzania delivery
  • East Africa ready
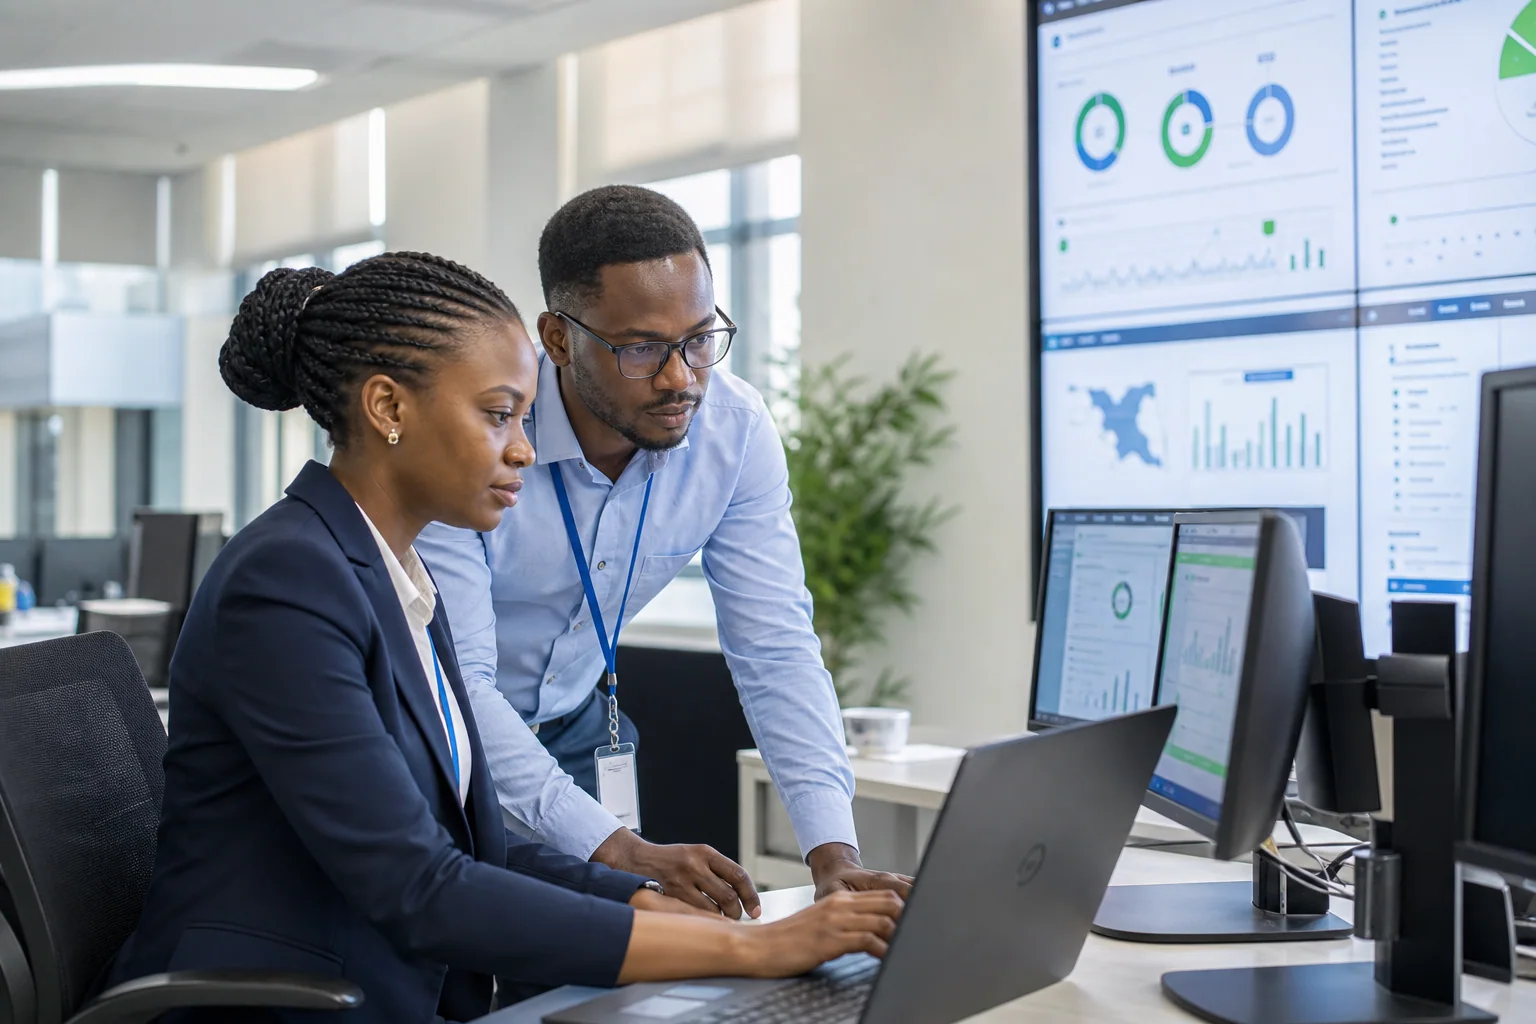
Concept illustration: Tanzanian security team reviewing operational risk, access controls and system monitoring
Delivery briefing A clear path from requirements to a working, supportable system. Concept illustration — not a product screenshot or evidence of delivered functionality.
01 Clarify Outcome, users and constraints
02 Design Architecture, workflow and controls
03 Deliver Build, adoption and accountable handover
Prioritise risk and define authorised access.

Use these questions to shape a useful first conversation. Scope and acceptance criteria are agreed for your project.

Best fit
An organisation reviewing website, application or infrastructure risks and recovery readiness.
Scope to agree
Agree authorised systems, testing boundaries, evidence handling, remediation and retesting.
Useful starting inputs
Bring an asset inventory, known incidents and access arrangements; never send passwords in a brief.
How to assess progress
Track agreed findings to remediation evidence and retest results; no system is risk-free.

A practical difference for your business

Know which security actions deserve attention first.

Unclear access, ageing configurations and untested backups create uncertainty; an authorised review can turn concerns into a practical improvement plan.

Replace uncertainty with a prioritised view

Security decisions are easier when the scope, findings and responsible people are clear. We review agreed systems with permission, explain the operational significance of findings and help plan selected corrections and recovery checks.

Illustrative use case (not a client result): An organisation could review administrator accounts and backup coverage, correct unnecessary access and test restoring an agreed set of records in a controlled environment.

Give the team an actionable security plan

  • An authorised assessment scope and evidence-based findings report.
  • Prioritised remediation tasks with owners and retest checks.
  • Access guidance and a recovery procedure for agreed systems.

Describe the systems you want reviewed without sharing passwords. We can define safe testing boundaries and a useful first assessment for your organisation. Scope a security review.

AI and cybercrime: learn from Watabe Digital

In AI & Cybercrime: Hatari Mpya kwa Biashara na Jinsi ya Kujilinda, Erick Angovi discusses AI-assisted phishing, fake invoices, voice impersonation and business preparedness. The Kiswahili video was published on Watabe Digital's official YouTube channel on 23 August 2026.

Use the discussion to prepare questions for your team:

  • Which important accounts have multi-factor authentication, and who owns access reviews?
  • How are unusual payment requests checked through a trusted, separate contact channel?
  • When was recovery from a backup last tested, and who recorded the result?
  • Do staff know how to report a suspicious message and who makes the next decision?

This is general awareness guidance. An assessment of your organisation requires an agreed scope, authorised access and evidence from your own environment.

Follow the related business cybersecurity discussion on Watabe Digital's LinkedIn, or explore Watabe Digital's official Instagram updates. To put the questions into a project, request a scoped security review.

What we can help with

Understand the risks. Make the next security action clear.

Strengthen the systems your organisation depends on through a defined assessment and improvement programme. We focus on authorised review, practical remediation and recoverability, with findings explained in operational terms and testing boundaries agreed before any work on your environment begins.

Investment, made clear

Turn the service into a clear investment

Compare relevant packages, included work and scope limits. Your final proposal is tailored to the requirements we agree.

Common Challenges We Address

  • Compromised staff accounts and ransomware threats stealing critical database information.
  • Undetected network vulnerabilities that expose SACCOS transactions to potential manipulation.
  • Failing mandatory compliance audits due to lack of standard security controls and policies.
  • Lack of cybersecurity awareness among employees, making them targets for social engineering.

Who This Service is For

Financial Cooperatives & SACCOS
Public & Government Institutions
E-Commerce & Digital Platforms
NGOs holding sensitive beneficiary data

Key Deliverables

Vulnerability Scanning & Pen Testing

Authorized ethical hacking tests on your web apps, APIs, networks, and server configurations to detect loopholes before malicious actors do.

Security Auditing & Assessment

Evaluating your IT environment against ISO 27001, BoT guidelines, and global security standards to identify policy gaps.

Incident Response Planning

Designing structured disaster recovery protocols, database restoration plans, and backup architectures.

Employee Cybersecurity Training

Practical workshops and phishing simulation campaigns to teach your staff how to identify and report threats.

Delivery Focus

Security & Reporting Modernization Pattern

This delivery pattern combines centralized access controls with prioritized vulnerability remediation to reduce exposure and improve audit readiness.

Read Case Study

Our Implementation Methodology

A standardized four-step consulting-led delivery model

01Discover

Initial Vulnerability Audit

We compile an asset inventory, analyze configurations, and scan for active vulnerabilities.

02Design

Threat Modeling

We map out potential entry vectors and design remediation priorities based on risk severity.

03Implement

Ethical Hacking & Test

We run penetration tests on designated environments, mapping access control gaps.

04Improve

Remediation & Governance

We deliver a comprehensive risk report, guide patch implementations, and run re-testing.

Expected Business Outcomes

Delivering measurable value for your operations

Lower digital-risk exposure through stronger access controls, remediation and monitoring.
Detailed, itemized vulnerability report with step-by-step remediation commands.
A documented assessment of the agreed controls, identified gaps and recommended remediation. Certification or regulatory acceptance depends on the applicable requirements and the responsible authority.
Highly vigilant workforce trained to spot and block phishing attempts.

Independent company feedback

Read Watabe Digital's company reviews on Clutch to understand client delivery experiences. Reviews are not a security certification or evidence that a particular system has passed an audit. Technical findings and remediation must be supported by evidence from the agreed assessment.

Read independent company reviews on Clutch

Ready to Drive Measurable Improvement?

Partner with Watabe Digital. We align strategy with robust software execution and cybersecurity.

Frequently asked questions

Clear answers before you decide.

What does this Watabe Digital service include?

Watabe Digital reviews practical security risk across access, infrastructure, applications, data handling, backups and continuity, then documents prioritized remediation actions.

Who is this service designed for in Tanzania and East Africa?

This service is intended for organizations that need to understand their current exposure, strengthen operational controls or prepare clearer security requirements for management and suppliers.

How does Watabe scope this service?

The engagement starts with a structured brief covering the intended outcome, users, current systems, constraints, integrations, evidence needs and decision timeline before a delivery plan is recommended.

Next step

Turn this capability into a scoped delivery plan.

Share the intended outcome, current constraint and decision timeline. Watabe will recommend the most useful next step.

Request a tailored proposal